OPEN SOURCE · SELF-HOSTED · INSPECTABLE

Own the stack.
Keep the answers.

Infrastructure tools should tell you what exists, what changed, what is failing, and what gets fixed first—without turning your evidence into somebody else’s subscription.

14 focused projects 100% open source 0 mandatory clouds

ONE SYSTEM · FIVE QUESTIONS

AIB
What exists—and what breaks?ASSETS · RELATIONSHIPS · IMPACT
OIB
What is it doing?SIGNALS · HEALTH · HISTORY
SIB
Is it hostile?RUNTIME · NETWORK · RESPONSE
VIB
What matters first?RISK · EXPLOITATION · EVIDENCE
IIB
Who and what is trusted?IDENTITY · PKI · ACCESS
XIB unifies the focused security-posture tools. Every project still works alone.
01Outcomes first

Start with the operational question, not a shopping list of containers.

02Blueprint, not black box

Every component, config, dashboard, and trade-off stays visible.

03Local by default

Your telemetry, findings, identities, and asset data remain under your control.

START HERE · ASSETS IN A BOX

Know the blast radius before production teaches you.

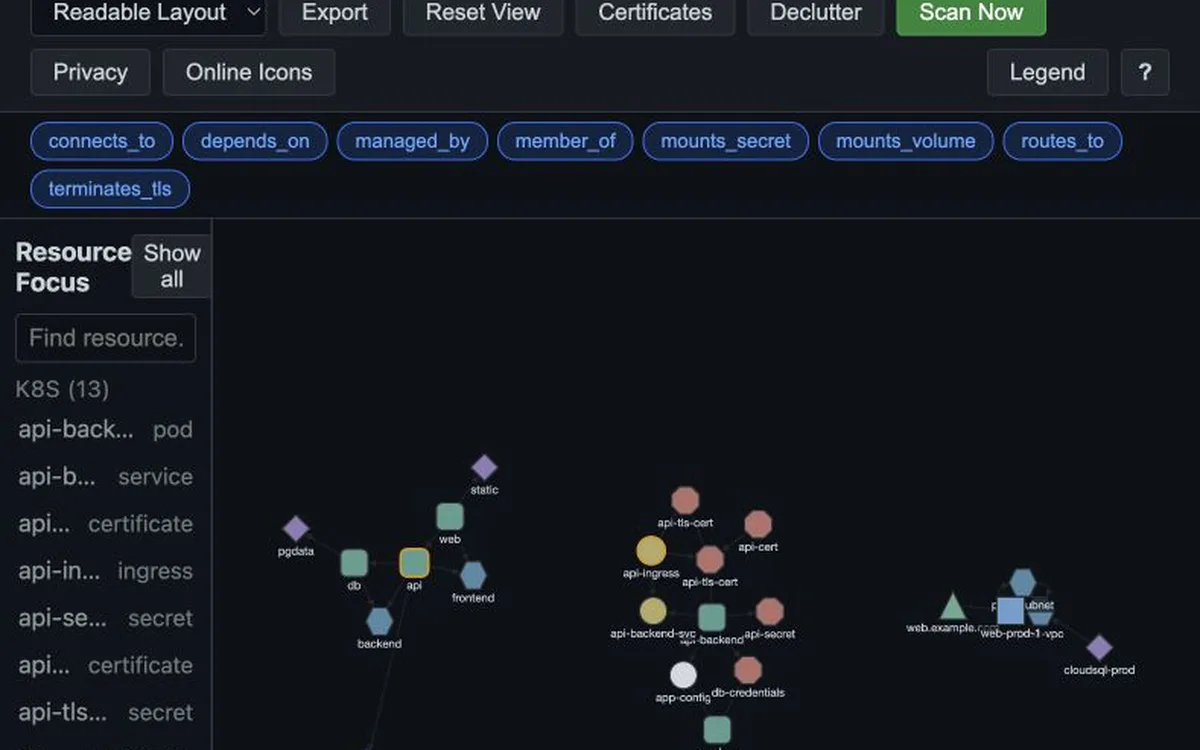
Your infrastructure is already documented—just not in one place. AIB turns Terraform, Kubernetes, Ansible, Docker Compose, CloudFormation, and Pulumi into a living dependency graph.

Ask what depends on a database, which workloads share a certificate, what changed between scans, or what a Terraform plan will disturb before the change becomes an incident.

aib / decision context
impactWhat breaks if prod-db changes?12 assets
driftWhat changed since the last scan?+3 / −1
auditWhich findings affect public paths?4 critical
spofWhere is failure concentrated?2 nodes

Configuration describes the pieces. AIB shows you the system.

RUNNING SOFTWARE · VISIBLE OUTPUT

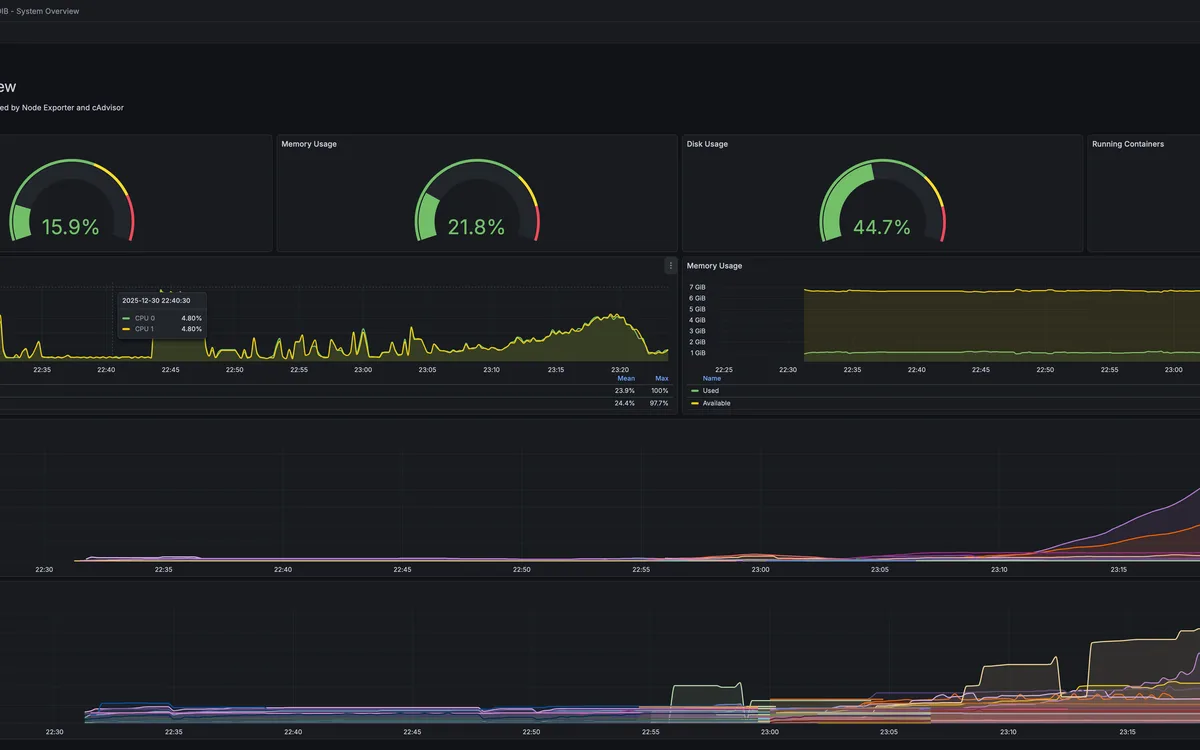
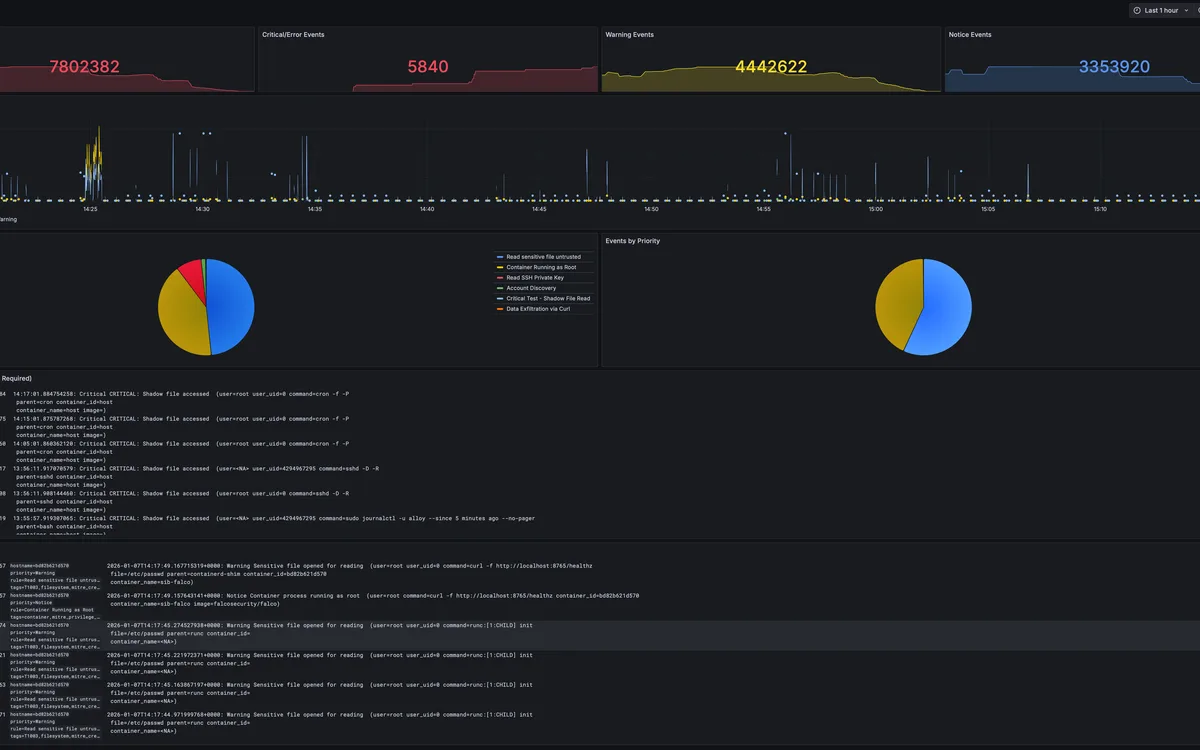
The screens exist. So does the scrutiny.

These are real outputs from the projects—not product mockups. The public repositories expose the dashboards, configuration, tests, and trade-offs behind them.

GitHub snapshot · 31 July 2026

THE COMPLETE TOOLKIT

Pick the question that hurts.

Use one focused blueprint, combine several, or deploy XIB for a unified security-posture view. No fake “single pane” promise: the individual tools remain understandable and independently useful.

Established — broader tests and validationActive blueprint — shipped and focused, with lighter verificationDeveloping — usable core with gaps stated plainly
01

Context & Operations

Understand the system and give teams a useful operating surface.

ORuntime evidenceEstablished

Observability in a Box

(OIB)

See what the system is doing without renting your telemetry back.

Run metrics, logs, traces, profiles, dashboards, health tooling, and instrumented examples as an understandable self-hosted stack.

12 validated stack variants · 50 GitHub stars

make bootstrapDetails →
DData platformActive blueprint

Database in a Box

(DIB)

Give developers real databases, real tooling, and a safe place to learn.

Five database engines, six web UIs, monitoring, backups, migrations, sample data, and connection helpers in one development platform.

CI-backed development and lab platform

make installDetails →
02

Detection & Response

Observe hostile behavior at the workload, cluster, and network layers.

CₐCloud audit SIEMDeveloping

Cloud Audit in a Box

(CAIB)

Keep the cloud audit trail. Keep the detections. Keep the evidence.

Collect, normalize, search, and detect across AWS, GCP, Azure, and Cloudflare on Vector, PostgreSQL with TimescaleDB, and Grafana.

70 tests · measured 1M-event benchmark · HA and restore drills

make demoDetails →
SRuntime securityEstablished

SIEM in a Box

(SIB)

Detect what workloads do, not merely what their logs claim.

Falco runtime detection, routed alerts, searchable security events, ATT&CK dashboards, fleet collection, and optional private AI analysis.

64 tests · 96 GitHub stars

make installDetails →
KKubernetes securityDeveloping

SIEM in a Box for Kubernetes

(SIB-K8s)

Bring runtime detection and explainable triage into the cluster.

A Helm-based Falco, Falcosidekick, Loki, Grafana, and optional AI-analysis stack for Kubernetes audit and runtime signals.

Core Helm stack shipped · roadmap edges disclosed

helm install sib-k8s .Details →
NNetwork securityDeveloping

NIDS in a Box

(NIB)

See hostile traffic before the incident report has to explain it.

Suricata inspection, CrowdSec behavioral detection, network dashboards, and deliberate host or router blocking modes.

11 GitHub stars · current CI gap disclosed
make installDetails →
03

Posture & Prioritization

Turn noisy findings into an ordered, evidence-backed queue.

VVulnerability postureActive blueprint

Vulnerability in a Box

(VIB)

Know which running images carry risk—and whether that risk is growing.

Discover running container images, scan them with Trivy, retain vulnerability history, and feed critical findings into AIB.

Recurring Trivy scans with retained history

TExploit prioritizationActive blueprint

Threat Intelligence in a Box

(TIB)

Fix the vulnerabilities attackers are actually using first.

Correlate VIB findings with CISA KEV and EPSS so active exploitation and probability—not CVSS alone—drive the queue.

CISA KEV and EPSS correlation shipped

CPolicy evidenceActive blueprint

Compliance in a Box

(CIB)

Turn container policy from a spreadsheet promise into evidence.

Check runtime configuration, SBOM licenses, and base-image end-of-life status while retaining CycloneDX evidence for review.

Runtime, SBOM, licence, and EOL evidence

04

Trust & Access

Control identity and certificate trust without outsourcing either.

IIdentity and SSOActive blueprint

Identity in a Box

(IIB)

Put one identity boundary in front of the services you operate.

Package Authentik with its data services, generated secrets, identity health metrics, and an operational Grafana view.

Authentik deployment with health metrics

PInternal PKIActive blueprint

PKI in a Box

(PIB)

Issue internal certificates automatically and catch expiry before users do.

Run step-ca with ACME support, trust-bootstrap helpers, endpoint probing, and certificate-expiry dashboards.

step-ca, ACME, and endpoint monitoring

HAI agent guardrailsDeveloping

Harness in a Box

(HIB)

Decide what your coding agent may touch, and see what left the machine.

A local harness over Claude Code and Codex with per-folder policy, a redaction guard, an egress log, approval prompts, and analysis that sends code instead of data.

Over 150 tests · Ubuntu and macOS CI · MIT

hib serveDetails →
Security Posture in a Box(XIB)

UNIFIED SECURITY POSTURE

One operational view across vulnerabilities, exploitation, compliance, identity, and PKI.

Compose VIB, TIB, CIB, IIB, and PIB with pinned submodules and a unified Grafana dashboard while keeping every tool independently deployable.

Vulnerabilities (VIB)Exploit priority (TIB)Compliance (CIB)Identity (IIB)PKI (PIB)

OPERATIONALLY HONEST

Not a magic button.
A better starting point.

The projects package real open-source components with explicit configuration, health checks, dashboards, examples, and operating commands. They reduce integration toil; they do not abolish capacity planning, threat modeling, backups, or knowing your environment.

That distinction matters. “Zero complexity” is marketing nonsense. Visible complexity with useful defaults is something an engineer can actually operate.

SELF-HOST IT OR GET HELP

Your infrastructure. Your data. Your call.

Every project is free to inspect, fork, and run. For architecture review, a hardened deployment, or ongoing operations, the engagement shape and deliverables are explicit.